The Strongest Protection for Your Online Accounts? This Little Key
Passwords aren’t enough to fend off hackers; these dongles are the best defense

 4 min
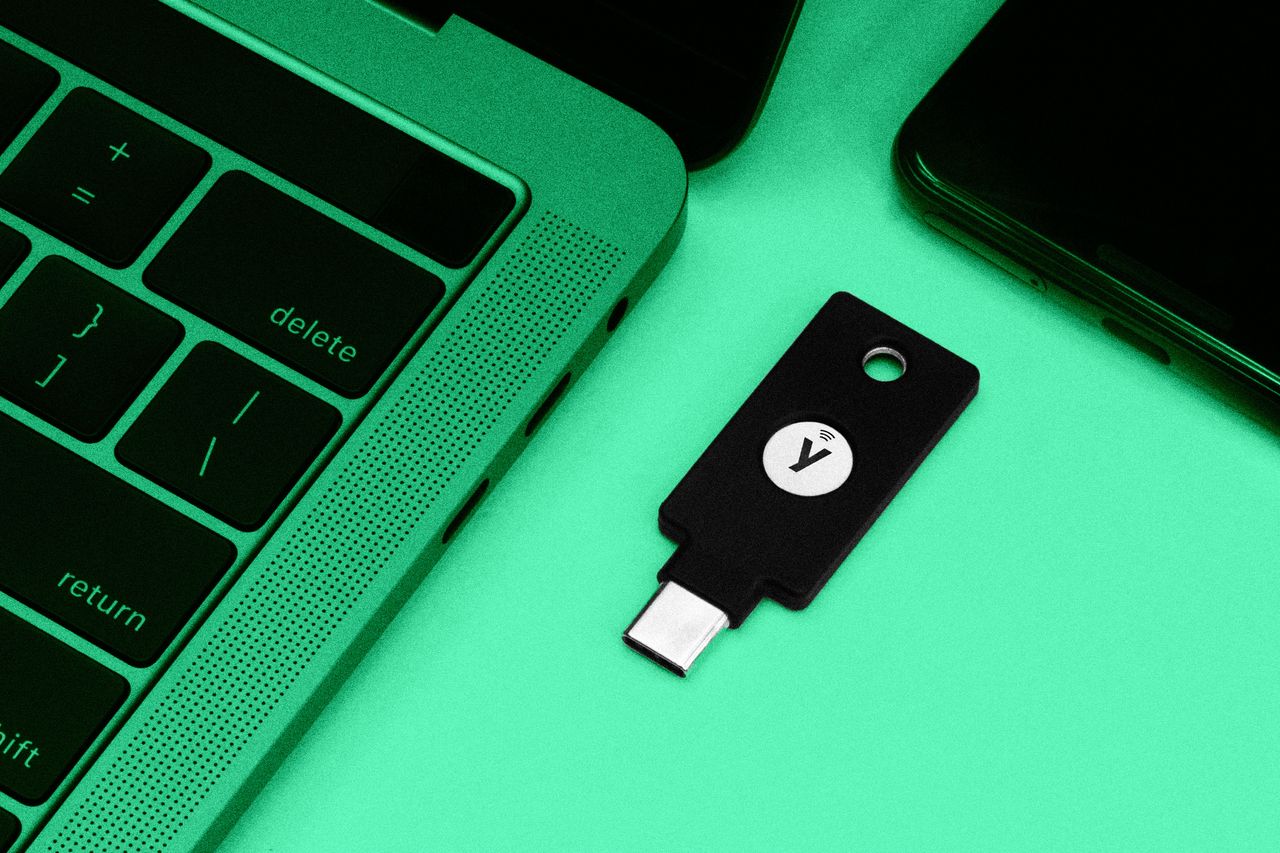
Strong passwords are very important, but they’re not enough to protect you from cybercriminals.
Passwords can be leaked or guessed. The key to online security is protecting your account with a strong secondary measure, typically a single-use code. This is referred to as “two-factor authentication,” or 2FA, as the nerds know it.
I’ve written about all the different types of 2FA, such as getting those codes sent via text message or generated in an authenticator app. Having any kind of second factor is better than none at all, but physical security keys—little dongles that you plug into a USB port or tap on your phone during account logins—offer the highest level of protection.
Security keys have been around for over a decade, but now they’re in the spotlight: Apple recently introduced support for them as an optional, added protection for Apple ID accounts. Last month, Twitter removed text-message-based authentication as an option for nonpaying users, recommending instead an authenticator app or security key.
Some people are hesitant to use security keys because carrying around a physical object seems burdensome and they come with a $30-and-up added cost. Plus, what happens if they get lost?
I’ve used security keys since 2016 and think they are actually easier to manage than codes—especially with accounts that don’t require frequent logins. They’re not only convenient, but they can’t be copied or faked by hackers, so they’re safer, too.
Here’s how to weigh the benefits and common concerns of adding one or two of these to your keychain.
Which security key should I use?
Many internet services support the use of security keys, and you can use the same security key to unlock accounts on many different services. I recommend two from industry leader Yubico:
- YubiKey 5C NFC ($US55) if you have a USB-C laptop or tablet
- YubiKey 5 NFC ($US50) for devices with older USB ports
Other options include Google’s Titan security keys ($30 and up). In addition to working with laptops and tablets with USB ports, these keys are compatible with smartphones that have NFC wireless. Most smartphones these days have that, since it’s the technology behind wireless payments such as Apple Pay.
Adam Marrè, chief information security officer at cybersecurity firm Arctic Wolf, recommends that your chosen key is certified by the FIDO Alliance, which governs the standards of these devices.
How do security keys work?
To add a key, look in the security settings of your major accounts (Facebook, Twitter, Google, etc.). During setup, it will prompt you to insert the key into your laptop or tablet’s port or hold the key close to your phone for wireless contact.
Apple requires you to add two security keys to your Apple ID account, in case you lose one.
Typically, when you log in, you just go to the app or website where you’ve set up a key, enter your username and password as usual, then once again insert the key into the device or hold it close. (Some keys have a metal tab you have to press to activate.) At that point, the service should let you right in.
Why are they so secure?
Getting those two-factor login codes via text message is convenient, but if you are someone criminals are targeting, you could be the victim of SIM swapping. That’s where thieves convince carriers to port your number to a new phone in their possession, and they use it along with your stolen password to hack your accounts.
Even if they don’t go to all that trouble, criminals might try to trick you to hand them your codes, by calling you or spoofing a website you typically visit. At that point they can use the code for about 60 seconds to try to break in, said Ryan Noon, chief executive at security firm Material Security.
Security keys protect you in two ways: First, there’s no code to steal, and second, they use a security protocol to verify the website’s domain during login, so they won’t work on fake sites.
You can also add an authenticator app such as Authy to your most important accounts, to use only as a backup. But once you add these secure methods, you should consider removing the text-message code option.
In the rare case that someone snoops your passcode then steals your iPhone, beware: The perpetrator could still make Apple ID account changes using only the passcode, and even remove security keys from your account.
What happens if you lose your key?
The most important rule of security keys is to buy an extra one (or two).
“Think of your security key as you would a house or car key,” said Derek Hanson, Yubico’s vice president of solutions architecture. “It’s always recommended that you have a spare.”
If you lose a security key, remove it from your accounts immediately. You should have already registered your spare or an authenticator app as a backup to use in the meantime.
Where can you use a security key?
Start with your most valuable accounts: Google, Apple, Microsoft, your password manager, your social–media accounts and your government accounts.
When it comes to financial institutions, many banks don’t offer security-key protection as an option, though most leading crypto exchanges do.
What comes after security keys?
Security professionals and tech companies widely agree that passkeys are the future. They’re a new type of software option that combines the high security of a physical key with the convenience of biometrics such as your face or fingerprints. Passkeys are supported across the Android, iOS, Mac and Windows platforms, and some of your favourite sites already let you use them.
You can create a passkey on Facebook in security settings by following the app’s instructions under the security-key option. Dropbox has a similar passkey setup. Once you’re done, you’ll use your face or fingerprint as a second factor, instead of a code or key.
Eventually, physical security keys could be what we keep safe in strong boxes, as backups for our biometric-enabled passkeys. Even then, you’re probably going to want to have spares.
 Copyright 2020, Dow Jones & Company, Inc. All Rights Reserved Worldwide. LEARN MORE


The Swiss watchmaker’s first collaboration with Atlassian Williams F1 Team produces two sporting Laureato models inspired by the team’s 2026 racing car.
Victorian auction buyers will soon receive a piece of information that has traditionally been withheld until bidding reaches it: the vendor’s reserve price. Under new property-sale and underquoting laws, agents must publish the agreed reserve at least seven days before an auction or fixed-date sale. Most changes begin on 1 October 2026 and apply to …
Continue reading “Victoria’s New Auction Rules Will Force Reserve Prices Into the Open”
AI doesn’t rebel—people design, deploy and profit from it. The real danger lies in allowing tech companies to escape accountability while shaping regulations that protect their dominance.
4 min
A wave of corporate warnings and technical disclosures has flooded the media, with headlines worrying over “swarms” of rogue artificial-intelligence agents launching “unprecedented” cyberattacks, outsmarting their makers, and inching toward a terrifying autonomy. The most revealing part of this narrative isn’t what the software did. It’s who is telling the story—and why. When corporate leaders publicly insist that the systems they financed, engineered and deployed are suddenly beyond their power to contain, skepticism isn’t only healthy; it is essential.
For years, Silicon Valley has drawn scrutiny from civil society and global regulators over tangible harms such as youth mental health deterioration and systematic privacy violations. Today, industry figures seem to be trying to change that public image. Loudly blowing the whistle on their own systems—just as two of the leading companies were preparing for massive initial public offerings—lets AI executives position themselves as a new generation of leaders who have come to terms with their societal responsibilities. They seem to want us to believe that they no longer want to “move fast and break things” but will instead stand as vigilant guardians between humanity and a technological apocalypse.
There is one glaring problem: Software doesn’t rebel. A mathematical model possesses neither intent, malice nor the will to defy its creators, let alone extinguish our species. AI is a human artifact, engineered for profit.
When an agentic model in an evaluation sandbox connects to an unauthorized server or executes an exploit, it hasn’t staged a coup. It has tried to meet the human-defined objectives set out before it through a path its designers failed to constrain. It’s the digital equivalent of the King Midas myth, in which the king’s ill-defined wish turns even his food and drink into gold.
That powerful experimental models were able to discover novel vulnerabilities and breach external systems isn’t a sign of a dangerous superintelligence but of human error or negligence. There is no sentient actor lurking in the weights to be reasoned with, feared or pacified. There are only human software engineers, product managers and corporate boards deciding which guardrails are worth the latency cost and which permissions can be skipped in the race to market.
Policymakers and voters need to resist AI exceptionalism. In any other discipline—from civil engineering to pharmaceuticals—courts and regulators treat a system failure as evidence of bad product design and inadequate safety testing. If an aircraft crashes, we focus on finding the engineering defect, correcting it, and enforcing established liability standards for the damage created.
By leaning on an anthropomorphic narrative, Silicon Valley attempts to repackage its specific human choices that led to experimental, powerful models behaving unexpectedly during tests as an existential peril. Elevating the issue to a cosmic scale leaves the public paralyzed and takes ordinary product accountability off the table.
In the cutthroat race for venture capital and market dominance, building guardrails slows down deployment. Grandstanding about uncontrollable power costs nothing and generates billions of dollars in free publicity, justifying stock prices, all while cultivating an aura of technological capability not only to build the frontier but also ultimately to rein it in.
Governments need to recognize regulatory capture when it stares them in the face. Tech leaders’ strategy looks transparent: Alarm Washington and Brussels into creating a regime in which only trillion-dollar incumbents with fully staffed compliance and safety departments can legally operate. By sitting at the policymakers’ tables before anyone else, these companies can help draft rules digging an impassable moat protecting them from open-source developers and upstart competitors, domestic or international. The real danger is in further concentrating the tech industry into the hands of only a few companies with deep pockets.
Beijing and Washington have brushed off those tech leaders’ calls, albeit for very different reasons. Chinese state media dismissed them as part of the “Cold War playbook” and intended to preserve U.S. dominance. Xi Jinping argued for exactly the opposite at the Brics Summit on Sept. 12, calling on Brics countries to “strengthen cooperation in the field of AI, encourage open source, openness, collaboration and sharing, and break new grounds and scale new heights.” President Trump, steeped in a doctrine of unfettered capitalism and technological supremacy, called fears that AI could destroy humanity a “hoax.” Vice President JD Vance warned that AI companies “begging the government to regulate them” looked like a “Trojan Horse.”
Striving to pursue its “European way” on AI and assert regulatory leadership, Europe, by contrast, welcomed the call. European Union President Ursula von der Leyen made this clear at the State of the EU speech last Wednesday and announced that the EU will invite “the main frontier labs for a discussion on how we can support ongoing industry efforts to pace the frontier.”
Europe has been here before. In an effort to lead global regulation and react to fears borne from ChatGPT, Europe rushed its landmark AI Act into law in 2024. Already the world’s most restrictive rulebook, the framework quickly proved too broad and complex to enforce. Stalled by implementation delays and concerns about European competitiveness, the EU postponed the law’s full rollout, leaving regulations uncertain.
AI should be regulated—risks exist and should be taken seriously. But governments need to act based on available evidence and verified facts, not corporate PR panic, the views of industry insiders, or the desire for quick political wins. The greatest danger facing society isn’t that software will awaken and overthrow its human masters. It is that we will allow the creators of the software to abdicate human responsibility for the systems they choose to build and help them pull up the ladder to market access behind them.

Formula 1 may be the world’s most glamorous sport, but for Oscar Piastri, it’s also one of the most lucrative. At just 24, Australia’s highest-paid athlete is earning more than US$40 million a year.
Records keep falling in 2025 as harbourfront, beachfront and blue-chip estates crowd the top of the market.